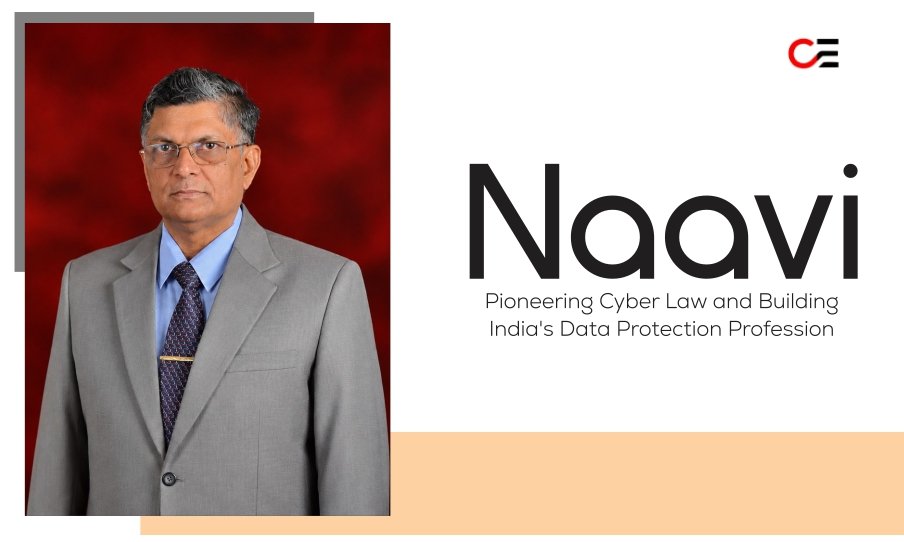
It is rare for one person to shape a field from three directions. Na. Vijayashankar, known to the data protection community simply as Naavi, has done so through three connected initiatives: the Foundation of Data Protection Professionals in India (FDPPI), the Data Governance and Protection Standard of India (DGPSI), and the Association of Independent Data Auditors (AIDAI).
Each answers a different question India must solve under the Digital Personal Data Protection Act, 2023 (DPDPA). Who will do the work of data protection? How should organisations go about it? And who will independently verify that it has been done?
Together, they reflect a vision that has consistently stayed a step ahead of the law.
From Banking Law to India’s Early Cyber Law Movement
Naavi’s professional journey began in 1973, when he joined Indian Overseas Bank as a Probationary Officer. During his banking career, he had a special stint at the Staff College, where he specialised in banking law. That experience later became a precursor to his interest in cyber law.
After moving from banking into the private sector, his interest in technology took him towards the internet. Cyber law gradually became an area of personal specialisation, and he began working in the field while India was still preparing its first information technology legislation.
In December 1999, while the Information Technology Bill was still pending and about ten months before the Information Technology Act, 2000 (ITA 2000) came into force, he published Cyber Laws for Every Netizen in India, widely described as the first book on cyber laws in India. His focus from then onwards remained on cyber law, e-commerce and related areas.
When ITA 2000 came into force, he established Cyber Law College, which he describes as India’s first virtual education institution. He also wrote further books on the subject, helping make an unfamiliar area of law more accessible to professionals and the public.
The early years were difficult. The country had a cyber law, but many of the people expected to use it did not understand its provisions. Members of the public hesitated to approach the police, adjudicators refused to take up civil complaints, and police stations frequently refused to entertain cybercrime complaints.
Naavi, who is not a lawyer, began to address this gap through education and practical legal intervention.
In 2004, State of Tamil Nadu v. Suhas Katti produced the first conviction under ITA 2000. Naavi provided the Section 65B certificate in the case, the first such certificate presented in an Indian court by his account.
Another significant development followed in Umashankar Sivasubramaniam v. ICICI Bank, a phishing case in which Naavi represented the victim under a Power of Attorney. On 12 April 2010, the Tamil Nadu Adjudicator held the bank liable and directed it to pay Rs 12.85 lakh.
These cases helped strengthen the recognition of cyber law as a practical area of legal work.
Alongside these developments, Naavi initiated a Cyber Law Awareness Movement across Karnataka, with several law colleges collaborating with Cyber Law College to spread awareness. Cybercrime police in Chennai and Bengaluru also adopted investigative practices aligned with the approach he advocated.
The work established an early foundation for the professional education and institutional development that later became central to his contribution to data protection.
FDPPI: Building India’s Data Protection Community
A new phase began in 2018. The Supreme Court of India had declared privacy a Fundamental Right in the landmark Justice Puttaswamy case in 2017, and the European Union’s General Data Protection Regulation (GDPR) took effect in May 2018. The Justice Srikrishna Committee report and the draft data protection legislation then brought the subject into sharper focus in India.
Naavi recognised that the country would need a dedicated professional community to understand, interpret and implement the emerging data protection framework. His response was FDPPI. He is the Founder Chairman and continues to lead FDPPI today.
FDPPI is a Section 8 company promoted by individual data protection professionals in India and headquartered in Bengaluru. Since its incorporation in September 2018, it has worked to develop the professional and institutional capabilities required for India’s data protection ecosystem.
The organisation began its certification programmes in 2019, when the country was still working with draft legislation. It was an early investment in professional skills, made before the law was enacted. As the regulatory framework evolved, FDPPI continued upgrading its programmes.
Its work has since expanded into education, certification, standards development, consultancy, research, policy advocacy and data auditing.
FDPPI’s underlying premise is that data protection requires participation across an organisation. Legal knowledge alone cannot establish a sound data protection culture. Technology, risk, compliance, management and business teams must understand their responsibilities and work together.
DGPSI: Turning Data Protection Law into Organisational Practice
A law establishes responsibilities, but organisations still need a practical way to fulfil them. This gap led to the development of the Data Governance and Protection Standard of India (DGPSI).
Conceived under the FDPPI umbrella, with Naavi as its chief architect, DGPSI provides frameworks to help organisations understand their DPDPA obligations and translate them into working systems.
The challenge lies in the diversity of organisations expected to follow the same law. A large enterprise, a small business, a hospital and a bank operate with different resources, risks, structures and data practices. A single template cannot serve them all equally well.
DGPSI therefore adapts to different organisational needs. Its versions include DGPSI-Lite for small and medium enterprises, DGPSI-HR for human resource operations, DGPSI-Hospital for hospitals and DGPSI-Banks for banking institutions. DGPSI-AI addresses data protection in an artificial intelligence environment, while DGPSI-DP offers a framework for voluntary adoption by Data Processors.
The initiative also extends to DGPSI-GDPR, which offers Indian entities an approach to GDPR compliance.
The thinking behind DGPSI has earlier roots. In 2009, Naavi proposed the Indian Information Security Framework, IISF-309. DGPSI carries that approach forward by bringing legal obligations, governance responsibilities and practical controls into a structured system.
One of its central principles is Distributed Responsibility. Data protection cannot rest with a single department or designated officer. Responsibilities must be assigned across the organisation, supported by documented processes, controls and evidence that can be examined.
DGPSI is also available as an open-source framework for organisations implementing DPDPA. Data Auditors can use it to assess implementation and calculate the Data Trust Score (DTS), a measure of an organisation’s data protection maturity.
DGPSI gives businesses a practical route towards compliance and gives auditors a common reference point for examining implementation.
AIDAI: Preparing for the Audits Ahead
Once organisations begin implementing a regulatory framework, the next requirement is independent examination. Compliance must be assessed by competent professionals, using consistent methods and reaching evidence-based conclusions.
Naavi’s attention to this stage led to the promotion of AIDAI in April 2026.
AIDAI is intended to develop independent data auditors as a professional community. Its work includes auditor empanelment and certification, professional collaboration, business exchange and a Code of Conduct to guide members.
The association has also developed a standard operating procedure for data audits across multiple units. Modelled on ICAI’s SA 600, it sets out how a lead auditor can rely on component auditors. This matters particularly for banks, whose extensive branch networks make consistent, repeatable audit methods essential.
The need for such a profession is expected to become more visible as DPDPA’s substantive provisions move towards full implementation. Section 10 of the Act requires Significant Data Fiduciaries to appoint an independent data auditor, creating a clear reason to prepare auditors and audit practices ahead of the implementation deadline.
For Naavi, AIDAI’s purpose is to help establish the foundations of a credible profession. Auditor competence, independence and consistent methods will determine the confidence organisations can place in data audits.
With a standard framework under DGPSI for compliance and an empanelled set of Data Auditors who can conform to a Code of Ethics, Naavi has laid the ground for development of Association of Independent Data Auditors of India (AIDAI) to take the new generation of Data Audit professionals into the emerging era of DPDPA in India.
Extending the Vision Through Data Valuation
Naavi’s work has also explored an area of growing relevance to organisations: the value of data.
FDPPI introduced the concept of Data Valuation in 2023 and developed a proof of concept through the Data Valuation Standard of India (DVSI). The initiative encourages organisations to treat data as an asset whose value can be assessed within a structured framework.
FDPPI reports interest in the concept from the Comptroller and Auditor General (CAG) and public sector undertakings.
Data Valuation adds another dimension to data governance. Organisations need to understand the data they hold, the responsibilities attached to it and the value it represents.
Looking Ahead to Artificial Intelligence and Neuro Rights
As artificial intelligence becomes part of business operations and public services, data protection faces new questions. AI systems introduce uncertain risks for Data Fiduciaries, particularly where personal information is used in training, decision-making and automated processes.
FDPPI has responded through DGPSI-AI, a framework for implementing DPDPA in an AI environment. Naavi has also been involved in developing the Artificial Intelligence Governance Standard of India (AIGSI), which enhances DGPSI-AI and could provide a foundation for future AI governance and legislation in the country.
Naavi points to similarities between DGPSI-AI’s recommendations and the Reserve Bank of India’s approach to AI governance. He expects the principles developed through AIGSI to find reflection in India’s future AI laws.
FDPPI has also raised the subject of Neuro Rights and the need for a Neuro Rights Protection Act, reflecting its interest in protecting individuals as technology increasingly interacts with human cognition and behaviour.
The underlying approach remains consistent: identify the governance requirements emerging from new technology and develop frameworks that help organisations respond responsibly.
Policy Advocacy and Engagement with the Regulatory Environment
FDPPI’s contribution also extends to policy advocacy. It has sought to intervene in two nationally significant legal matters: a WhatsApp case before the Delhi High Court and the challenge to DPDPA’s constitutionality before the Supreme Court.
In both matters, FDPPI has supported the Government’s approach and opposed arguments it considers disruptive to DPDPA’s implementation.
FDPPI has also engaged with government and regulatory bodies, including MeitY, CERT-In and the Bureau of Indian Standards, at different stages of its development.
As DPDPA’s implementation progresses, FDPPI expects its role in professional development and industry support to become more prominent.
A Philosophy of Collective Growth
Naavi’s approach to leadership rests on three qualities: the vision to identify what is right, the conviction to pursue it even when standing alone, and the persistence to continue along a path where few have ventured before.
His personal philosophy, “Jala Vridhya, vardhate Padmam,” adds another dimension. The phrase conveys the idea that as the water in a pond rises, the lotus rises with it. Individual growth, in this sense, follows the growth of the larger environment.
He describes FDPPI as his child and takes pride in the effort he has invested in it. Yet, like a father who takes pride in seeing his child grow, he is more interested in the institution’s development than in his own promotion.
He hopes FDPPI’s progress will encourage more people, more Naavis, to emerge in data protection and other fields, creating a wider community able to take responsibility and carry the work forward.
A Legacy Built for the Next Generation
India’s data protection journey will continue to evolve through new laws, technologies and professional requirements. DPDPA will develop through its application, while AI governance and changes to ITA 2000 may open further areas of legal and institutional work.
Naavi’s contribution can already be seen in FDPPI, DGPSI, AIDAI and DVSI, along with the ongoing work on AIGSI. FDPPI develops the professionals, DGPSI provides the implementation framework and AIDAI supports independent scrutiny.
His journey, from banking in 1973 to cyber law, digital education and data governance, reflects a consistent instinct: anticipate where the law and industry are heading, and build what people will need for the next stage.
A founder may begin the journey with an idea, but an institution gains its real strength when others take ownership of its growth. For Naavi, that is the larger achievement: building a foundation on which an entire professional community can rise.